Google Workspace
The Keep Aware integration with Google Workspace syncs your Workspace users, groups, and group memberships into Keep Aware. Once synced, you can assign those groups to Profiles to distribute policy and scope threat responses to the right people and browsers.
Requirements
- Keep Aware console access: Sign in to the Keep Aware console with valid credentials.
- Google Workspace admin access: Use a Google Workspace super-admin, or an admin with directory-read privileges. This admin authorizes the connection, and the sync runs with that admin's read access.
Getting started
Connecting Google Workspace is a single step: an admin authorizes Keep Aware from your Keep Aware console. Keep Aware then runs the first sync and refreshes your Google groups on a schedule.
Keep Aware reads your directory only. It requests three read-only scopes and never writes back to Google Workspace. Once synced, your Google groups appear on the Groups page and can be referenced in Profiles to scope policy and threat responses to specific people and their browsers.
Most organizations can connect directly. If your organization blocks unconfigured third-party apps, an admin needs to trust the Keep Aware app once first — see Restricted third-party app access.
Connect Google Workspace
Connect the integration from your Keep Aware console:
- In the Keep Aware console, go to the Integrations page.
- In the Group Management section, select the Google Workspace card.
- In the dialog that opens, click Create new integration to open the configuration page.
- The configuration page has no fields to fill in. Click Save. The Google consent screen opens.
- Sign in as your Google Workspace admin and approve the read-only scopes Keep Aware requests.
There are no fields to fill in for this integration. Unlike some integrations, Google Workspace doesn't ask you to paste a URL, key, or secret — the configuration page opens with no fields, and clicking Save takes you to Google's consent screen. If the page looks empty, that's expected; nothing is missing.
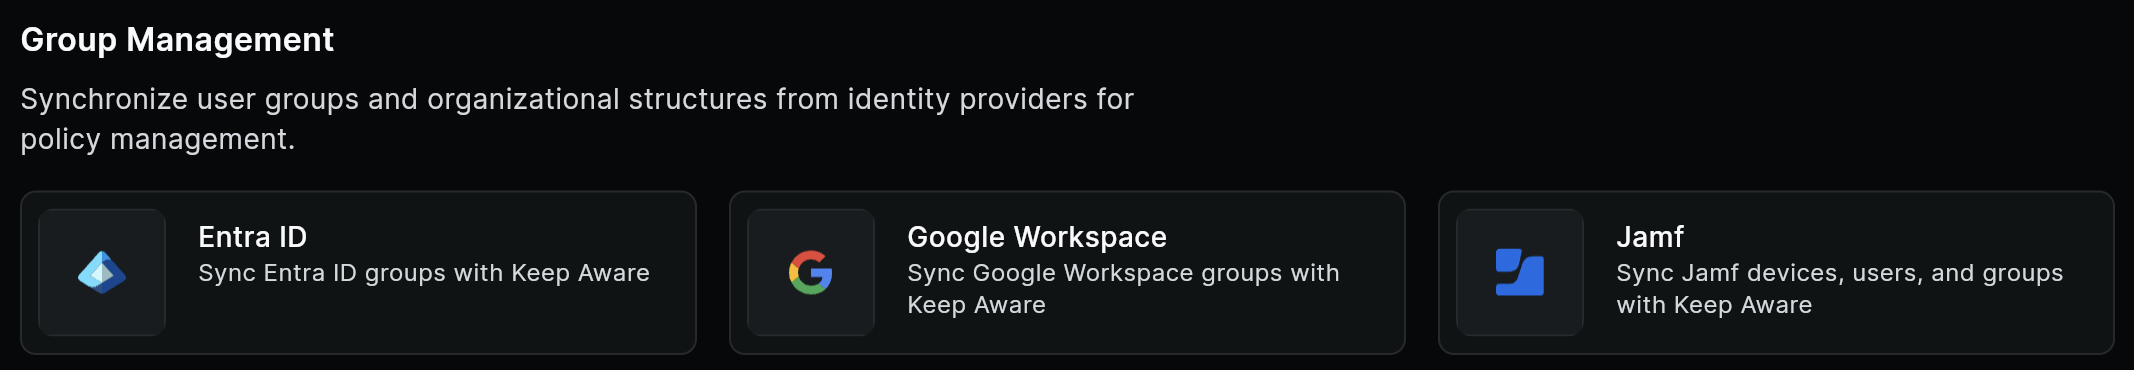
Image: the Google Workspace card in the Group Management section of the Integrations page
Restricted third-party app access
Most organizations can skip this section. Google Workspace lets admins control which third-party apps can access organization data. If your organization blocks unconfigured third-party apps by default (or uses Context-Aware Access), an admin with app-access-control rights must mark the Keep Aware app Trusted before the connection in the previous step will succeed.
- In the Google Admin console, go to Security, then Access and data control, then API controls.
- Under App access control, click Manage app access, then Configure new app.
- In the OAuth App Name Or Client ID search box, look up Keep Aware by name and select the app. If it doesn't appear, contact your Keep Aware account team.
- Set the app's access to Trusted.
- Confirm that the app is granted the three read-only directory scopes:
https://www.googleapis.com/auth/admin.directory.user.readonlyhttps://www.googleapis.com/auth/admin.directory.group.readonlyhttps://www.googleapis.com/auth/admin.directory.group.member.readonly
- Save your changes, then connect the integration as described in Connect Google Workspace.
All three scopes are read-only. Keep Aware reads your users, groups, and group memberships and never modifies anything in Google Workspace.
How the sync works
Keep Aware reconciles your Google Workspace directory on a schedule and updates the matching users, groups, and memberships in Keep Aware.
- Keep Aware syncs your Workspace users, groups, and group memberships.
- The integration is read-only: Keep Aware requests only the three
*.readonlydirectory scopes and never writes back to Google Workspace. - Keep Aware stores a single per-tenant credential, so only one admin connects the integration.
- Group membership changes reflect in Keep Aware after the next scheduled sync, not in real time.
Frequently asked questions
| Question | Answer |
|---|---|
| Does Google Workspace sync in real time? | No. Keep Aware reconciles your directory on a schedule, so membership changes appear after the next sync. |
| Will this change anything in Google Workspace? | No. The integration is read-only. Keep Aware reads your users, groups, and memberships and never writes back. |
| Do I need to enter any credentials or settings? | No. The configuration page has no fields — just click Save to open Google's consent screen. |
| Do I need to trust or allow-list the Keep Aware app? | Only if your organization blocks unconfigured third-party apps. Most organizations can connect directly; restricted organizations follow Restricted third-party app access. |
| What scopes does Keep Aware request? | Three read-only directory scopes: admin.directory.user.readonly, admin.directory.group.readonly, and admin.directory.group.member.readonly. |
Support
Setting up Google Workspace happens in your Keep Aware console, with an optional step in the Google Admin console for organizations that restrict third-party apps. If you have trouble approving the scopes, trusting the app, or the sync doesn't return the groups you expect, reach out to your Keep Aware account team for help.